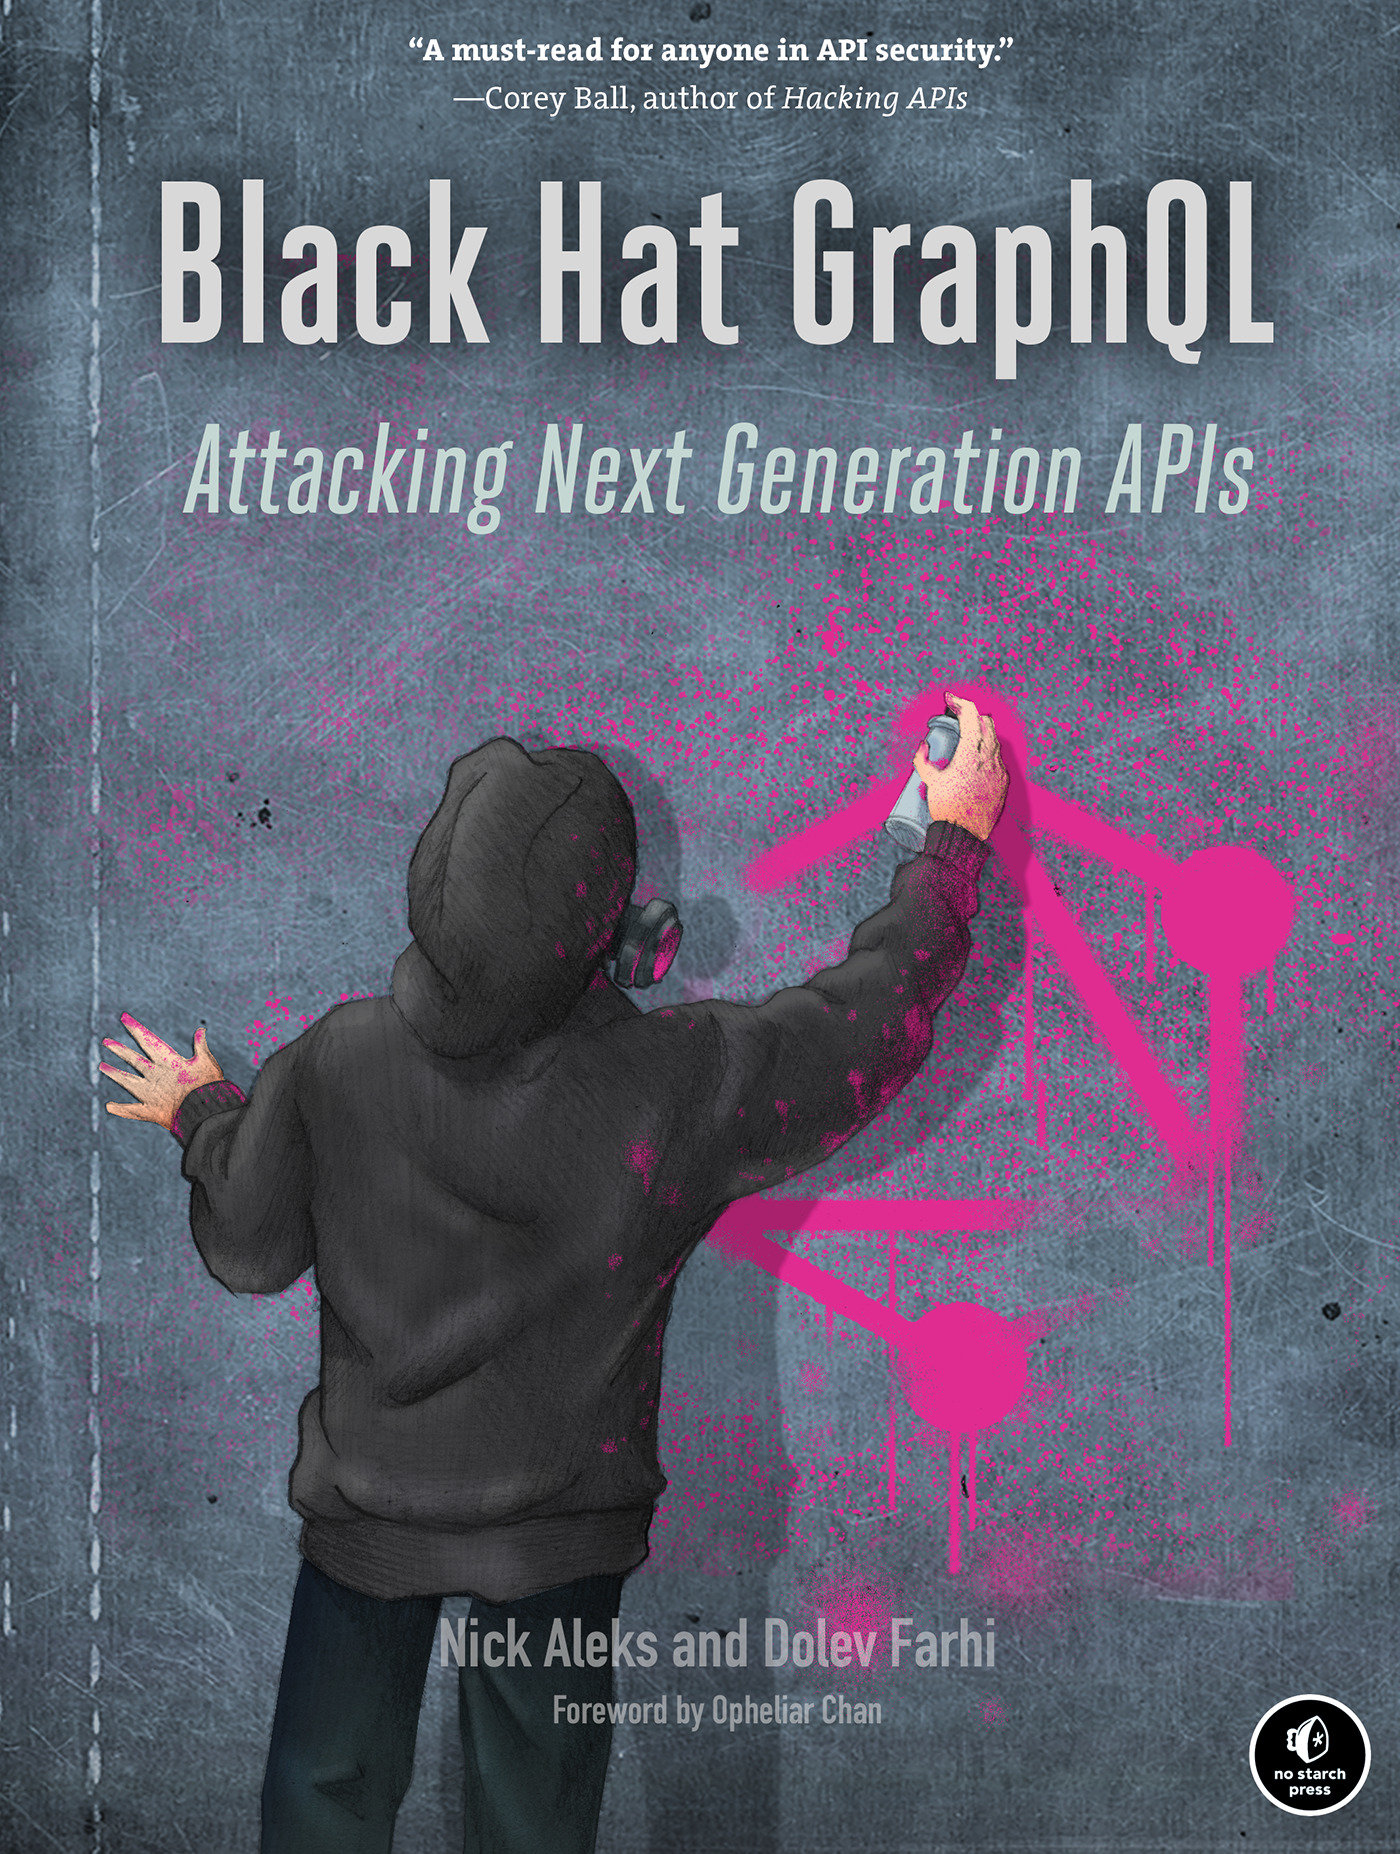
Black Hat GraphQL
Attacking Next Generation APIs
No Starch Press · Print & ebook · May 23, 2023
Written by hackers for hackers, this hands-on book teaches penetration testers how to identify vulnerabilities in apps that use GraphQL, a data query and manipulation language for APIs adopted by major companies like Facebook and GitHub.
We earn from qualifying purchases.
- Who it’s for
- Explore GraphQL API attacks and defenses, from custom queries to secure development practices.
- Themes
- GraphQL API security, Penetration testing, Secure software development
- Genres
- Computer Security, APIs & Web Services, Network Security
Nearest books
Matched by what the books are about, then ordered by what their readers also loved.
 Hacking APIsCorey J. Ball73% matchShares Computer Security and APIs & Web Services
 Social EngineeringChristopher Hadnagy54% matchShares Computer Security and Network Security
 Black Hat Python, 2nd EditionJustin Seitz, Tim Arnold53% matchShares Network Security
 CORS in ActionMonsur Hossain51% matchShares APIs & Web Services
 Graph DatabasesIan Robinson, Jim Webber51% match
 Haskell in DepthVitaly Bragilevsky50% match
 The Complete DeveloperMartin Krause50% matchShares APIs & Web Services
 Secure by DesignDaniel Deogun, Dan Bergh Johnsson50% matchShares Computer Security
For younger readers: Slaying Digital Dragons ™, The CS Detective
Start with three books, and this one can be the first.
Members get a new edition every morning: a route out from their books to essays, research and talks, with the reason for each.
Start with this bookAbout this book
Written by hackers for hackers, this hands-on book teaches penetration testers how to identify vulnerabilities in apps that use GraphQL, a data query and manipulation language for APIs adopted by major companies like Facebook and GitHub. Black Hat GraphQL is for anyone interested in learning how to break and protect GraphQL APIs with the aid of offensive security testing.
Continue reading
Whether you’re a penetration tester, security analyst, or software engineer, you’ll learn how to attack GraphQL APIs, develop hardening procedures, build automated security testing into your development pipeline, and validate controls, all with no prior exposure to GraphQL required. Following an introduction to core concepts, you’ll build your lab, explore the difference between GraphQL and REST APIs, run your first query, and learn how to create custom queries. You’ll also learn how to: - Use data collection and target mapping to learn about targets - Defend APIs against denial-of-service attacks and exploit insecure configurations in GraphQL servers to gather information on hardened targets - Impersonate users and take admin-level actions on a remote server - Uncover injection-based vulnerabilities in servers, databases, and client browsers - Exploit cross-site and server-side request forgery vulnerabilities, as well as cross-site WebSocket hijacking, to force a server to request sensitive information on your behalf - Dissect vulnerability disclosure reports and review exploit code to reveal how vulnerabilities have impacted large companies This comprehensive resource provides everything you need to defend GraphQL APIs and build secure applications. Think of it as your umbrella in a lightning storm.
GraphQL API Security
Explore GraphQL API attacks and defenses, from custom queries to secure development practices.
Come here for
- GraphQL queries, target mapping, and vulnerability discovery
- API hardening, pipeline testing, and control validation
Expect
- A lab setup and comparison of GraphQL and REST APIs
- Coverage of denial-of-service, injection, and request-forgery vulnerabilities
Where it sits
| APIs & Web Services | 71% |
|---|---|
| Computer Security | 45% |
| Network Security | 37% |
Percentages are BookFrontier’s reading of the book.
Publisher categories
- Network Security
- Web Programming
- APIs & Web Services
- Authors
- Nick Aleks, Dolev Farhi
- Publisher
- No Starch Press
- Published
- May 23, 2023
- Format
- Print & ebook
- Theme
- GraphQL API security · Penetration testing · Secure software development
- Reading lane
- Network Security